


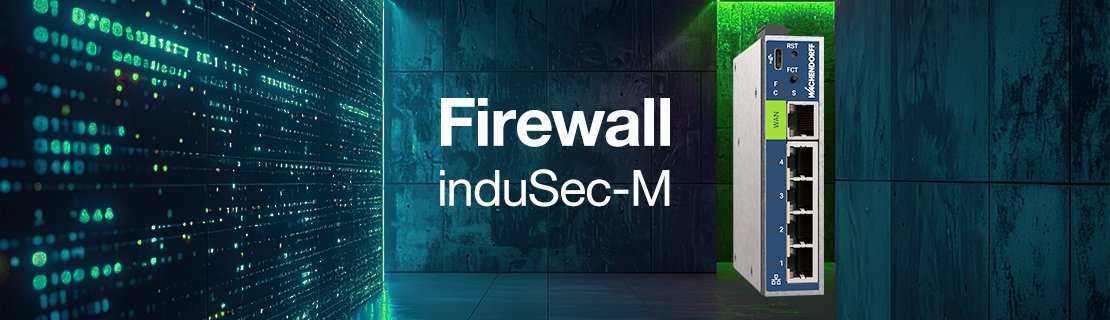

Industrial Firewall and NAT Gateway – induSec-M
Secure Machine Integration and Targeted Network Segmentation
The Wachendorff induSec-M combines an industrial stateful firewall with a NAT Gateway to secure and integrate machine and plant networks. Flexible NAT functions, network segmentation, and controlled communication enable the easy integration of standardized machines into existing customer networks.
As an OT security Gateway at the machine level, the induSec-M supports a comprehensive defense-in-depth strategy. Modern security mechanisms and professional IT management interfaces enable controlled and secure communication between machine, production, and IT/OT networks.
Security Made in Germany
Hardware, system architecture, operating system, software, and security concepts are designed and developed holistically in Germany. This results in a unified platform in which hardware, software, and security are coordinated from the very beginning.

Security by Design in accordance with IEC 62443
Development is carried out in accordance with the requirements of IEC 62443-4-1 for a secure product development process. Secure Boot, signed firmware, and hardware-based key protection are central components of the security concept. The goal is to achieve product certification in accordance with IEC 62443-4-2, Security Level 3.

Professional IT Compatibility and Monitoring
SNMPv3, MQTT API, and REST API enable integration with existing IT/OT management systems, as well as monitoring and configuration. IEEE 802.1X, when used as a Client, enables authenticated and controlled network access.

Simplified setup with the firewall learning mode
The learning mode analyzes existing network traffic and helps users create appropriate firewall rules. Detected communication paths are presented as rule suggestions and can then be reviewed and approved on a case-by-case basis.
Expected to be available starting in Q2 2027.

Stateful Firewall and Network Segmentation
Stateful packet filtering using IP, port, protocol, and MAC filters, as well as event-based firewall rules, enables targeted control of network traffic. Port-based VLANs also allow for the segmentation of individual LAN ports.

Abgesicherter Inselbetrieb
Eventbasierte Firewall-Regeln ermöglichen den Wechsel in einen definierten, abgesicherten Betriebsmodus. Dieser kann über I/Os sowie MQTT- und REST-API ausgelöst werden, um Kommunikationsverbindungen gezielt einzuschränken.

Flexible NAT Features & Operating Modes
, 1:1NAT, network NAT, masquerading, and port forwarding enable the integration of standardized machine networks. Gateway and transparent bridge modes offer flexible deployment options.
Compact Gigabit Industrial Hardware
Five Gigabit Ethernet ports—one WAN and four LAN—a housing width of just 27 mm, and an operating temperature range of −40 °C to +75 °C make this device ideal for compact installation in a control cabinet.
Applications and Customer Benefits
Standardized Machine Integration Without IP Addressing
Machine and equipment manufacturers often use standardized network configurations with fixed IP addresses. This can lead to IP address conflicts when integrating into different customer networks or when operating multiple machines of the same design. The induSec-M enables machines to be integrated into different customer networks via 1:1 NAT and network NAT while retaining their original internal IP addressing. This allows PLCs, HMIs, and other components to maintain their original network configuration.
Your benefit: Reduced engineering and commissioning effort thanks to standardized machine configurations.
Securing Machine Networks with a Firewall and Network Segmentation
The increasing interconnectivity of machines requires controlled communication between different network segments. The integrated stateful firewall and port-based network segmentation allow you to establish defined security boundaries between machine and production networks. Individually configurable firewall rules make it possible to allow only the necessary communication connections and block unwanted access.
Your benefit: Controlled machine communication and targeted restriction of unwanted network access.
Retrofitting Existing Machines with an Industrial Firewall
Many existing machines do not have their own network firewall. Retrofitting security measures often involves considerable effort if existing IP addresses or control configurations need to be changed. Through transparent bridge operation, the induSec-M can be integrated into existing network structures without having to fundamentally change their IP addressing.
Your benefit: Retrofitting network security with minimal impact on existing machine and plant configurations.
Easy integration into existing IT/OT infrastructures
Industrial firewalls must be able to integrate not only into the machine but also into the operator’s network infrastructure. The induSec-M offers modern management interfaces for this purpose, such as SNMPv3, REST API, and MQTT API. These enable integration into existing monitoring and management systems and support centrally organized monitoring and administration. A planned firewall learning mode is also intended to simplify the detection of existing network communication and the creation of appropriate firewall rules in the future.
Your benefit: Integration into existing IT/OT management processes and, in the long term, reduced effort required for firewall configuration.
Note: Firewall learning mode is expected to be available starting in Q2/2027.
Targeted Decoupling of Production from the Network During Security Incidents
In the event of a security incident, it may be necessary to temporarily disconnect a machine or system from the higher-level production network. Using event-based firewall rules, the induSec-M can automatically switch to a predefined set of rules for isolated operation and selectively restrict external communication connections.
Your benefit: Controlled network isolation while still allowing defined local machine functions to continue operating.

 to top
 Contact
 Request form